

Security & Compliance Consulting and Implementation for Companies
Security & Compliance Consulting and Implementation for Companies
Full-Lifecycle Protection
We manage security and compliance throughout the process, from planning and construction to operations and assessment.
In-depth Industry Experience
A reusable, extensible solution, developed from best practices in finance, e‑government, and other highly regulated sectors, ensures high compliance.
Technical & Compliance Designs
Security architectures with integrated compliance policies ensure system security and meet regulatory standards.
Intelligent Risk Control
Our tools and security monitoring models efficiently identify, handle, and audit risks.
Extensive Experience With Cloud Security and Stability in International Projects
Extensive Experience With Cloud Security and Stability in International Projects
20,000+ professionals
Staff with comprehensive security and privacy protection capabilities
2,700+ customers
Customers in 150+ countries and regions
16% market share
A market leader in the security consulting field

A Large, Professional Cybersecurity and Compliance Team
Deloitte has more than 20,000 cybersecurity and privacy professionals worldwide with well-rounded capabilities, including strategy development, compliance, technology implementation, and operations.
Customers Worldwide Across Diverse Industries
Deloitte's cybersecurity and compliance services are available in more than 150 countries and regions, serving more than 2,700 customers in major sectors, including finance, energy, e-government, manufacturing, and healthcare.
Leading Market Share in the Global Security Market
Drawing on thousands of security and compliance projects worldwide, Deloitte has developed reusable architectures in compliance with DJCP MLPS, ISO 27001, privacy protection regulations (for example, GDPR), and industry regulations to help you streamline compliance management.
Cloud Security and Compliance in Any Context
Cloud Security and Compliance in Any Context
Complex Regulatory Requirements for Financial Institutions
- Banks often face internal compliance requirements, local regulations, and cross-border regulations.
- Frequent compliance checks across business lines leave organizations pressed for time.
- Inconsistent internal standards drive up compliance costs.
- Establish a corporate-level security and compliance governance system, a standard framework that enforces unified policies, processes, and control requirements.
- Identify differences between local regulations and international standards, and develop a remediation plan.
- Use tools to solidify compliance checks, store evidence, and generate reports for internal and external audits.
- The compliance rectification period can be significantly shortened, easing the burden of multi-party inspections.
- The risks of fines and compliance incidents can be mitigated to enhance supervision and market confidence.
- Unified corporate internal control standards can be enforced to reduce compliance management costs in the long run.
Security and Compliance of Cloud Migration and Hybrid Clouds
- Enterprises are accelerating their migration to cloud and multi-cloud architectures, but traditional security controls and compliance requirements cannot be adapted easily.
- Without a unified view of cloud permissions, data flows, and logs, organizations struggle to demonstrate cloud compliance in audits.
- Design a cloud architecture with intrinsic security and compliance, including the account system, network partitions, access control, and logging and audit policies.
- Develop a compliance control matrix mapping DJCP MLPS, ISO, and internal policies for the cloud environment, and integrate it into cloud security baselines and templates.
- The cloud environment is visible, controllable, and auditable, helping organizations meet supervision and third-party audit requirements more easily.
- Cloud misconfigurations and security incidents on the cloud can be reduced, accelerating service migration and strengthening confidence.
- Templates can be reused to reduce compliance costs and allow you to migrate systems to the cloud faster.
Privacy and Cross-Border Data Compliance
- Companies operating across regions have to comply with local privacy regulations and cross-border data transfer requirements.
- Data classification and grading, access control, and approval processes are not well developed.
- Count data assets. Establish a unified data map and sensitive data catalog.
- Design a privacy and data compliance control system.
- Develop assessment and approval processes, supported by technical controls.
- The legal and reputational risks from privacy breaches and cross-border data violations are mitigated.
- The transparency and controllability of data use are improved.
- Companies can quickly complete compliance assessment and implementation when expanding business in a new region.
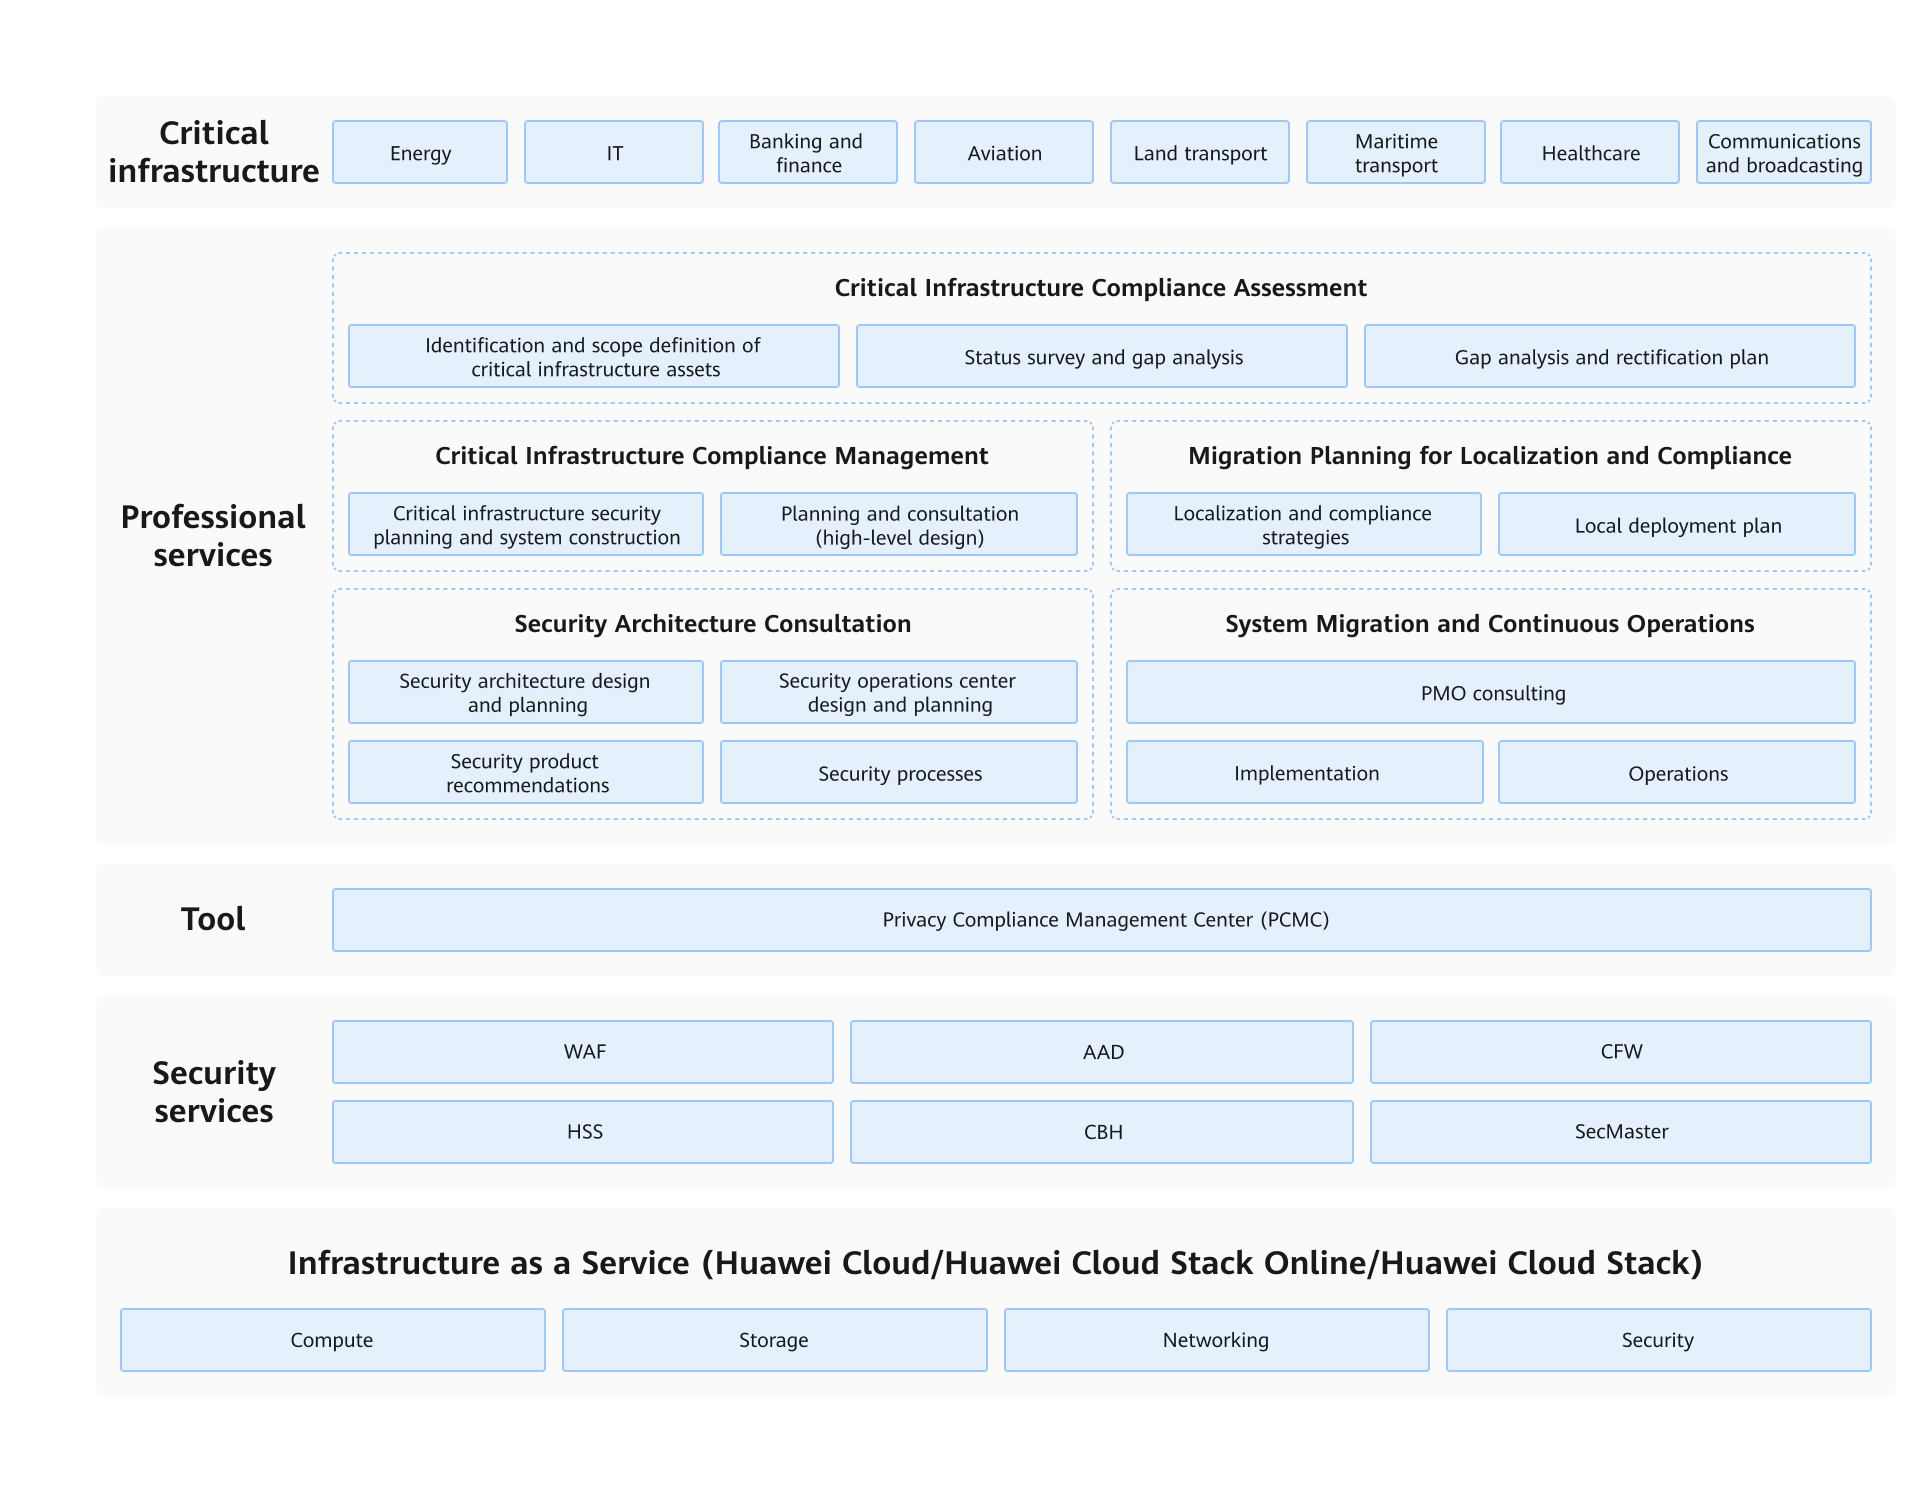
One-stop Critical Infrastructure Compliance Solution
One-stop Critical Infrastructure Compliance Solution
Join Hands With Industry Partners for Faster Development
Join Hands With Industry Partners for Faster Development
Deloitte Advisory (Hong Kong) Limited
As an integral part of Deloitte's global network, Deloitte Advisory (Hong Kong) Limited delivers comprehensive high-quality services for multinational corporations, local businesses, and institutions, drawing on its professional capabilities and deep industry experience.
- Deloitte Advisory (Hong Kong) Limited
As an integral part of Deloitte's global network, Deloitte Advisory (Hong Kong) Limited delivers comprehensive high-quality services for multinational corporations, local businesses, and institutions, drawing on its professional capabilities and deep industry experience.


